Federal agencies operate under some of the most stringent physical security standards in the world. With FedRAMP® Moderate Authorized status and government-grade access control offerings, Verkada is delivering modern, cloud-first physical security built specifically with these rigorous government requirements in mind.
Today, we are excited to announce FIPS 201 (FICAM) capabilities for Verkada Access Control in GovCloud. Unlike many legacy access control systems that require agencies to purchase, patch, and maintain separate hardware and software stacks to manage PIV credentials, Verkada delivers PIV card support natively in Command. This gives federal organizations a single cloud platform for registering PIV, PIV-I, and CAC credentials, authenticating cards at the door, and automatically deactivating untrusted, revoked, or expired cards.
In addition to adding FIPS 201 (FICAM) support, Verkada is queued for approval for the FIPS 201 Approved Products List (APL). The submission to the GSA covers our government-grade controllers (AC12-G, AC43-G, AC62-G) and readers (AD34-G, AD64-G), alongside the Veridt Stealth Dual PIV contact reader. Supporting FIPS 201 PIV card reads represents a major milestone that reflects our commitment to bringing uncompromising, modern physical security to federal agencies and military installations operating under FICAM.
PIV Credential Management in Command
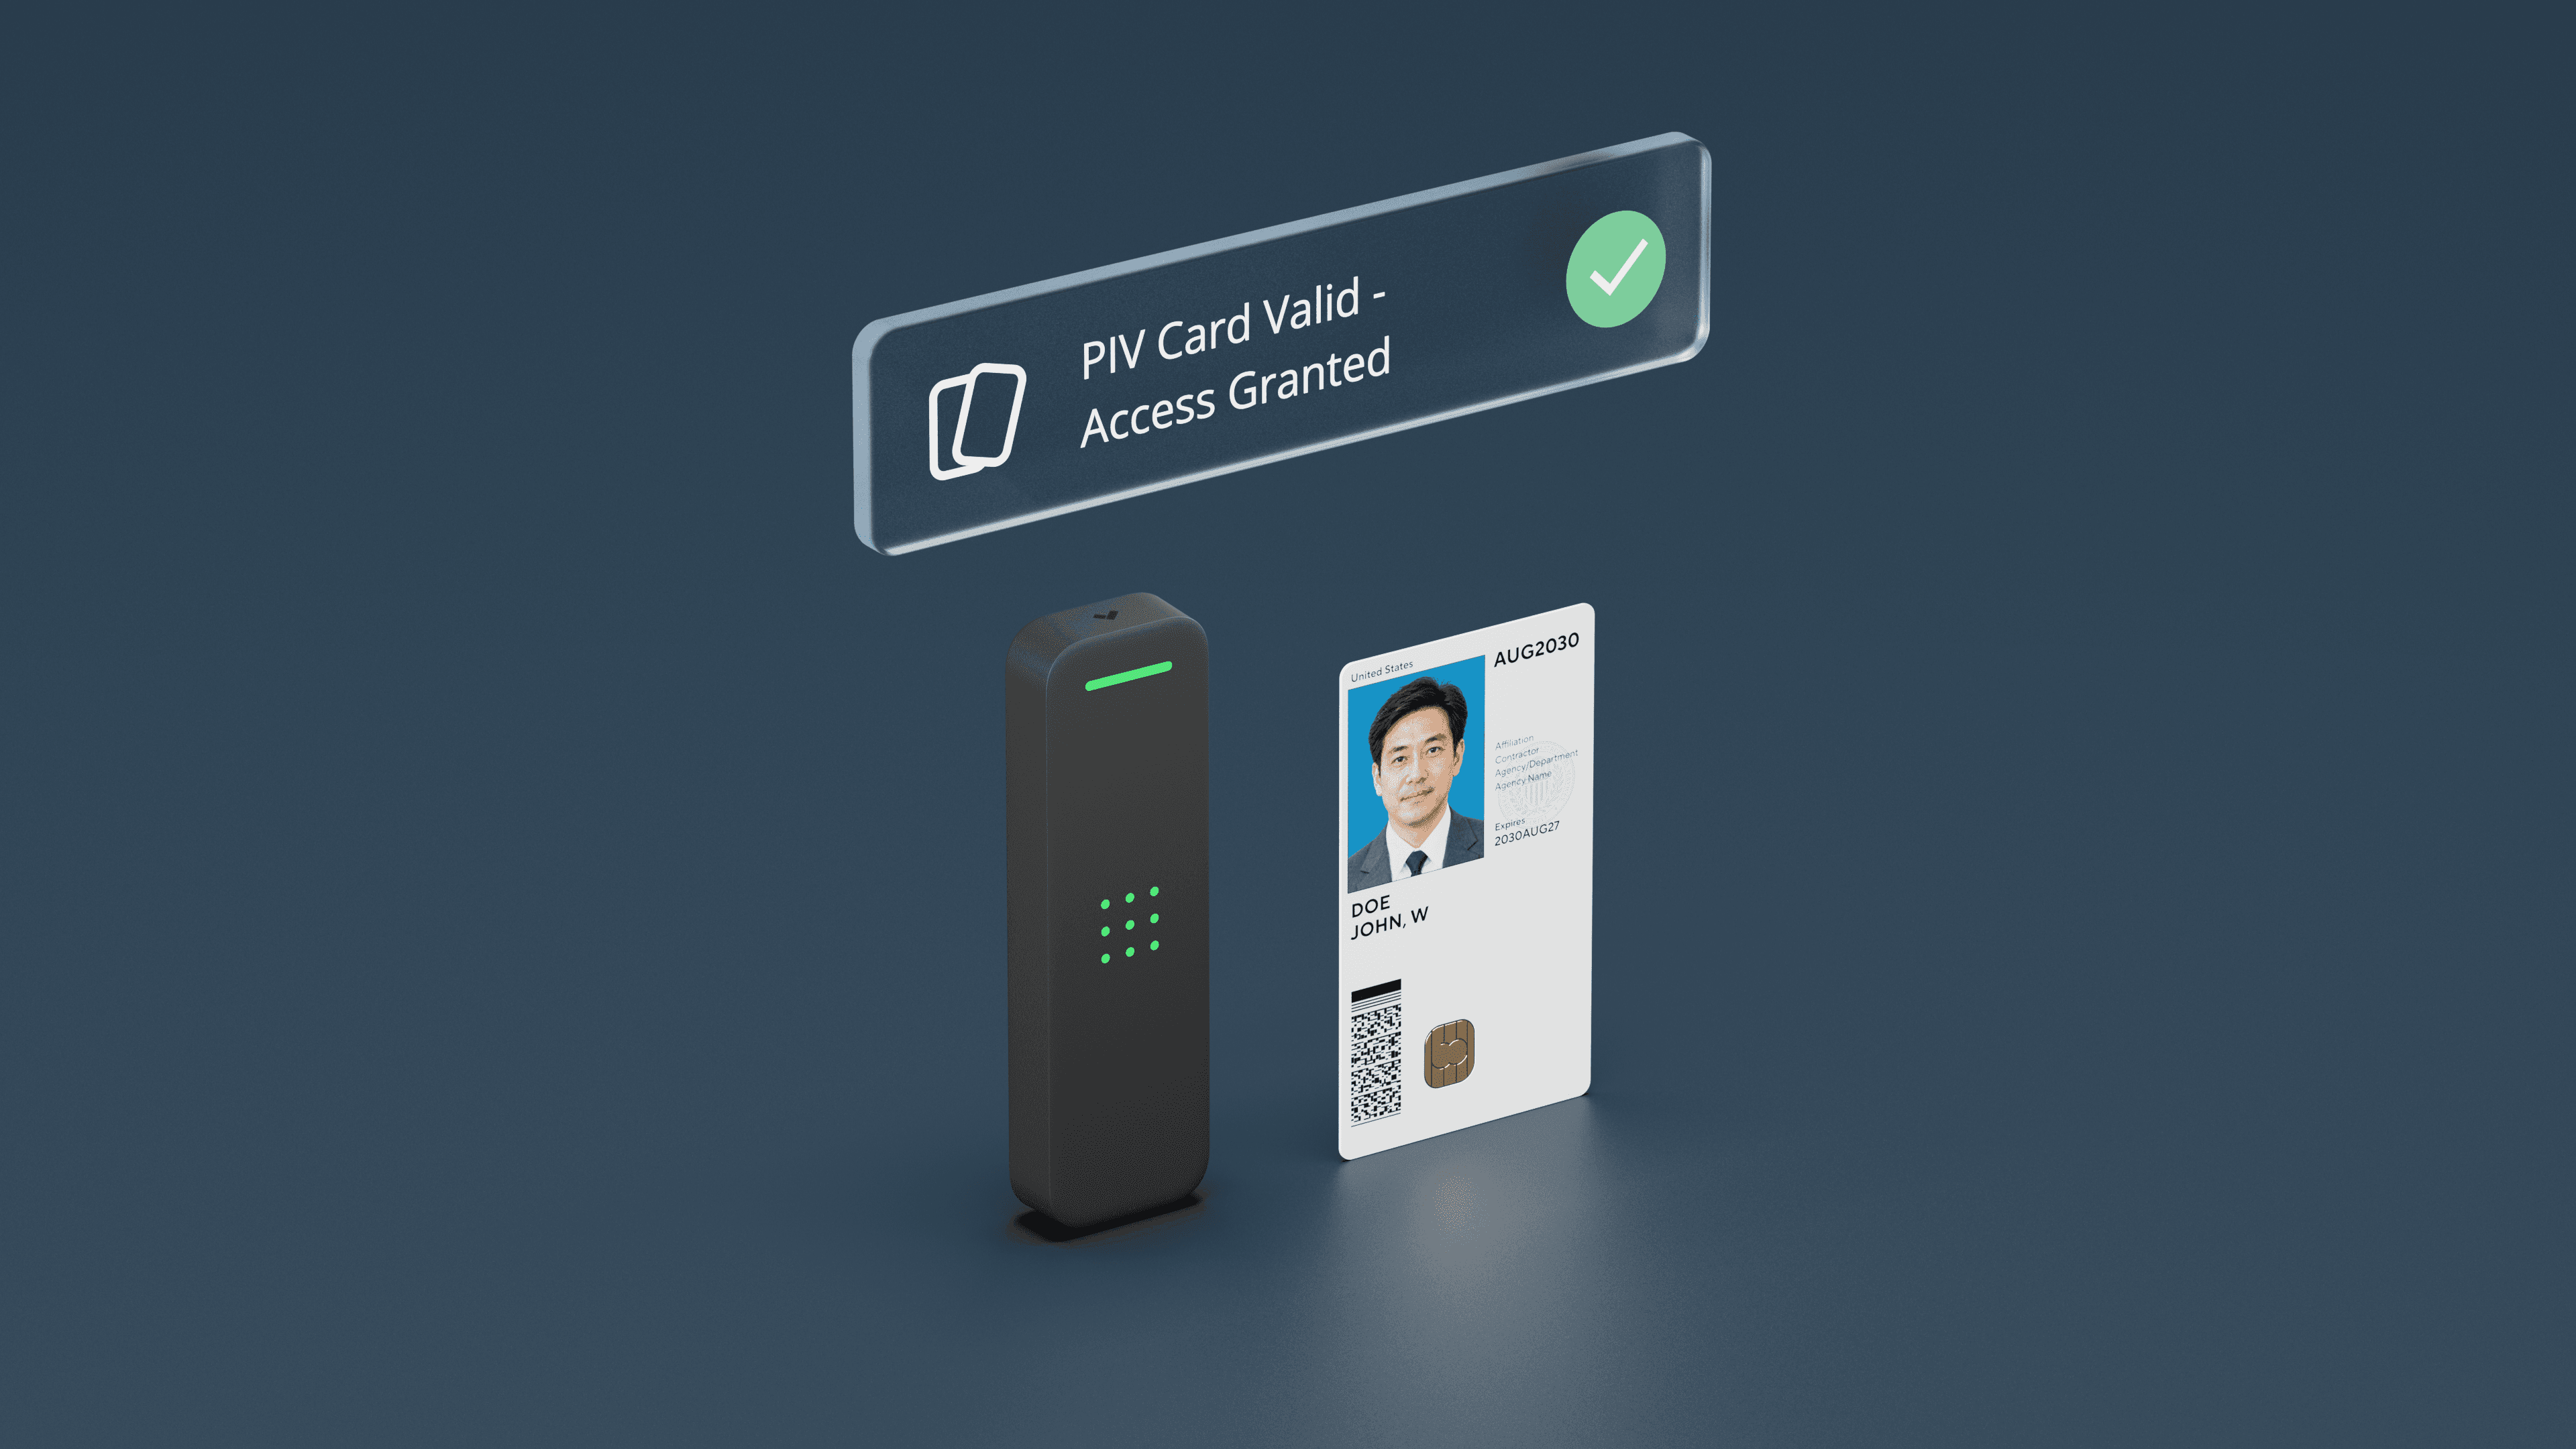
Verkada Command in GovCloud delivers full-lifecycle PIV credential management from enrollment to revocation, without the separate validation systems that many legacy platforms require.
Card registration: Admins can enroll new cardholders with the Veridt Stealth Dual PIV contact reader (ACCX-AC-PV-VT-1). During enrollment, Verkada performs real-time checks to verify the card is trusted, unexpired, and unrevoked, helping confirm that registered credentials align with FIPS 201 standards before being added to a user’s profile.
Certificate management and trust anchors: Access is limited to cards whose certificates chain to a trusted root. Federal and DoW roots are supported by default, and admins can upload additional trust anchors as needed.
Ongoing certificate revocation checks: Verkada regularly checks registered credentials in the background for revocation or expiration status. If a certificate is revoked or expired, or its chain of trust is broken, Command disables the card and removes door access.
Authentication at the door: Card scans trigger a cryptographic exchange between the card and the controller to verify that the card is genuine before access is granted, helping to prevent credential spoofing.
Hardware Portfolio and Deployment Configurations
Delivering government-grade physical security involves specialized hardware and firmware across access controllers and readers.
Access controllers: Verkada’s government-grade door controllers (AC12-G, AC43-G, AC62-G) are TAA and FY2019 NDAA compliant, and run specialized firmware using a FIPS 140-validated cryptographic module for on-device processing.
Card registration readers: Veridt Stealth Dual PIV contact readers handle in-person card registration, which requires physical card insertion and PIN entry. The readers connect to a Verkada access controller, so admins can enroll cards directly from Command.
Door access readers: Verkada access controllers pair with Verkada or Veridt readers, depending on each door’s security requirements. Supported readers communicate with Verkada access controllers over Secure Channel OSDP v2.
Verkada readers: Our government-grade access readers (AD34-G, AD64-G) are TAA and FY2019 NDAA compliant and support contactless one-factor PIV authentication (PKI-CAK). For an added layer of security, the AD64-G can also require users to enter an MFA code set in Command. This code is separate from the PIV card’s PIN, which requires a Veridt contact reader.
Veridt Stealth readers: For doors that require two-factor PIV authentication, organizations can deploy Veridt Stealth Dual PIV contact readers, where cardholders insert their PIV card and enter its PIN (PKI-AUTH).
By combining native PIV card support with our FedRAMP® Moderate Authorized environment, government-grade hardware, and intuitive cloud-managed platform, Verkada Access Control offers federal agencies a modern solution while elevating site security.
Availability
FIPS 201 (FICAM) functionality – including PIV card registration, automated card certificate revocation checks, certificate management, and support for Veridt contact readers – is expected to be available to Verkada GovCloud customers in November 2026. To learn more about our government-grade solutions and procurement options, please contact [email protected].
This blog post contains forward-looking statements. Please keep in mind that forward-looking projections are subject to change, including general release timeline, product features and functionalities, certifications, and pricing.


